By default, the broad Mail.Send graph api permission was/is often used for applications/managed identities to send emails.
Obviously it is quite rarely the case that an SPN has to be able to send email as ANY user in your tenant…
So for DriftMaester at least, this has now been corrected by removing the Mail.Send permission and instead using an Exchange Online custom RBAC assignment scoped to only the email you specify 🙂
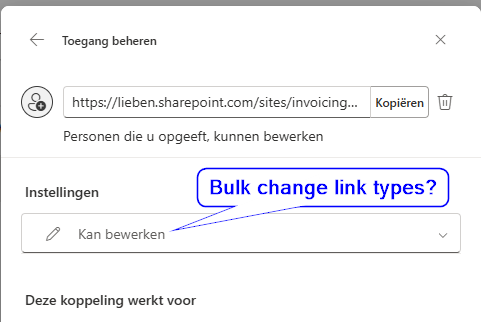
Sharing links in Onedrive/Teams/Sharepoint can be of the View, Edit, Review or No Download type.
There is no official Graph API or PnP module call that can be done to modify a link, it has to be done manually in the GUI as per Microsoft.
That didn’t work for me, as I’m working on some migration scenario’s where all links have to keep working, but should not allow users to edit or download the files.
So I did some digging, turns out there is a ShareLink GetSharingInformation endpoint that can be called for any object.
And with good ‘ol Claude, a script was built and tested in half an hour that iterates over a given sharepoint site(s) or a specific file and adjusts the link. I’ve made it configurable and use certificate based auth, enjoy!
How do you know who the original owner of a Onedrive site was?
The url says a lot, it’s usually in a username_domain_com format. If you have a fixed naming structure and don’t use _’s or other characters that are translated to _, it can be reversed with reasonable accuracy, right?
But what if you have two people with the same name? Or did some migrations or takeovers? Then your logic breaks 🙁
So reverse engineering the URL won’t work, and if an admin takes ownership or if the user leaves and the manager gets ownership, the Owner/Full Control ACL on the site also won’t tell you who the original owner was because it overwrites the Owner property.
In M365permissions the option to audit ownership of Onedrive is built in, as this is a common question during certain types of audits.
But how did we solve it there?
Well, it turns out that Sharepoint’s own metadata service maintains a pretty good track record of who was ever a user on a site, even after they are deleted from Entra.
Thus by doing a call to /_api/web/siteusers?$orderby=Id, we get a nicely ordered list of all users ever assigned to the site.
Pick the first non-system user, and we have our original user! See above 🙂
So there’s this problem with lots of Microsoft API’s not allowing service principals to call them. I’ve written about this a few times in the past 🙂
These api’s want a user. And a user has to do MFA, right?
Not with this!
When I read Nathan McNulty’s LinkedIn post this morning I got a bit hyped and just HAD to get it working. He has a way to use a stored passkey to log in silently to all admin portals/hidden api’s etc.
The missing part I wanted to solve, is to actually generate that passkey for a given global admin in the tenant.
Took a bit of messing around with how to generate the keys using a virtual authenticator, but it works! Here it is: